Information Security from the Attacker's Perspective
We combine information security with many years of experience in offensive cybersecurity. As penetration testers, we consistently examine systems from an attacker’s perspective: How are attacks carried out, which vulnerabilities can actually be exploited, and which measures are effective in practice?
This perspective shapes our approach. We develop ISMS, security strategies, risk analyses, and organizational measures not theoretically, but based on real risks and the operational reality within the company. In doing so, we take into account existing processes, responsibilities, resources, and industry-specific conditions.
We work based on established standards and regulatory requirements such as ISO/IEC 27001, BSI IT-Grundschutz, B3S, DORA, NIS2, and Critical Infrastructures, and translate these into practical, implementable structures.
Making Compliance Sustainable and Cost-Effective
Achieving compliance is manageable. The real challenge lies in making it effective over the long term, sustainable, and cost-effective. After all, compliance always becomes an integral part of the organization—with established processes, controls, responsibilities, and ongoing effort. It is therefore crucial, right from the outset, to create a framework that is sustainable in the long term and can be integrated into the operational reality.
Our approach is geared toward creating appropriate, efficient, and sustainable structures. In doing so, we take into account not only the required level of maturity but also the company’s organizational, operational, and economic conditions.
We evaluate security measures not only in terms of their formal compliance, but also in terms of their actual effectiveness, feasibility, and their contribution to reducing relevant risks.
Our Values in Consulting:
Team Sports
We work with our clients as equals and see ourselves as part of the team. Together, we tackle challenges and deliver measurable results.
Cost-Effectiveness
We take into account effort, resources, and costs, and strike an appropriate balance between security levels, regulatory requirements, and economic viability.
Pragmatism
We focus on what matters most and develop safety structures that are not only documented but also understood, applied, and put into practice in our day-to-day operations.
Expertise
Our consultants hold relevant certifications and have project experience in ISO/IEC 27001, BSI IT-Grundschutz, B3S, DORA, and NIS2, and can assist with both specific issues and the full implementation of complex security and compliance projects.
Choose the plan that's right for you:
01
Workshop
We analyze a specific issue, provide clarity, and work together to develop solid next steps.
02
Ad hoc consulting
We bring our expertise to bear wherever you need additional know-how, an independent assessment, or support with implementation on short notice.
03
Long-term support
We provide your organization with ongoing support in the areas of strategy, governance, and implementation, and are available to serve as a professional sounding board.
04
Outsource IT Security
Upon request, we can handle key or all aspects of information and IT security, ranging from regulatory requirements and risk management to day-to-day security operations.
Ihre Ansprechpartner
Sicherheit ist Vertrauenssache. Bei uns sprechen Sie nicht mit einem Ticketsystem – sondern direkt mit erfahrenen Experten.
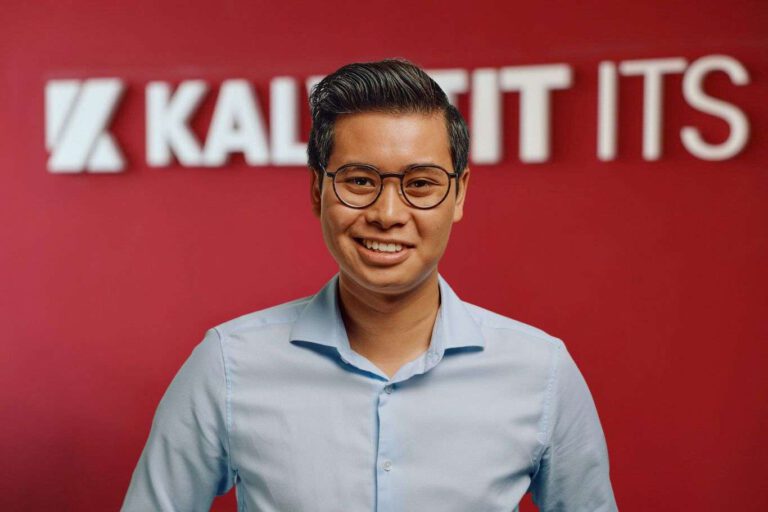
Philipp Kalweit ist Gründer und geschäftsführender Gesellschafter der KALWEIT ITS. Sein Beratungsschwerpunkt liegt auf Cybersecurity im Banken- und Versicherungsumfeld sowie bei kritischen Infrastrukturen (KRITIS). Seine unternehmerische Laufbahn begann mit 16 Jahren, als er mit einer Ausnahmegenehmigung des Amtsgerichts sein Hobby zum Beruf machte. Ein Jahr später gründete er das heutige Unternehmen. 2019 wurde er von DIE ZEIT als „Hamburger des Monats“ ausgezeichnet, auf der Titelseite des FOCUS-Magazins porträtiert und in die Forbes-Liste „30 Under 30“ aufgenommen.
S. Philipp Kalweit
Geschäftsführender Gesellschafter

Dipl.-Wirtsch.-Ing. Günther Paprocki ist seit 2024 geschäftsführender Gesellschafter der KALWEIT ITS und verantwortet die Bereiche Operations und Personal sowie die organisatorische Weiterentwicklung des Unternehmens. Zuvor war er in verschiedenen Positionen bei Sharp, Philips und Cisco tätig und wirkte an der Einführung und dem Aufbau bedeutender Technologien mit, darunter frühe Mobilfunknetze und Internetinfrastrukturen. Heute bringt der gebürtige Münchner seine langjährige Erfahrung in Personalführung, Prozessgestaltung und Technologieentwicklung in die Weiterentwicklung unseres Unternehmens ein.
Günther Paprocki
Geschäftsführender Gesellschafter